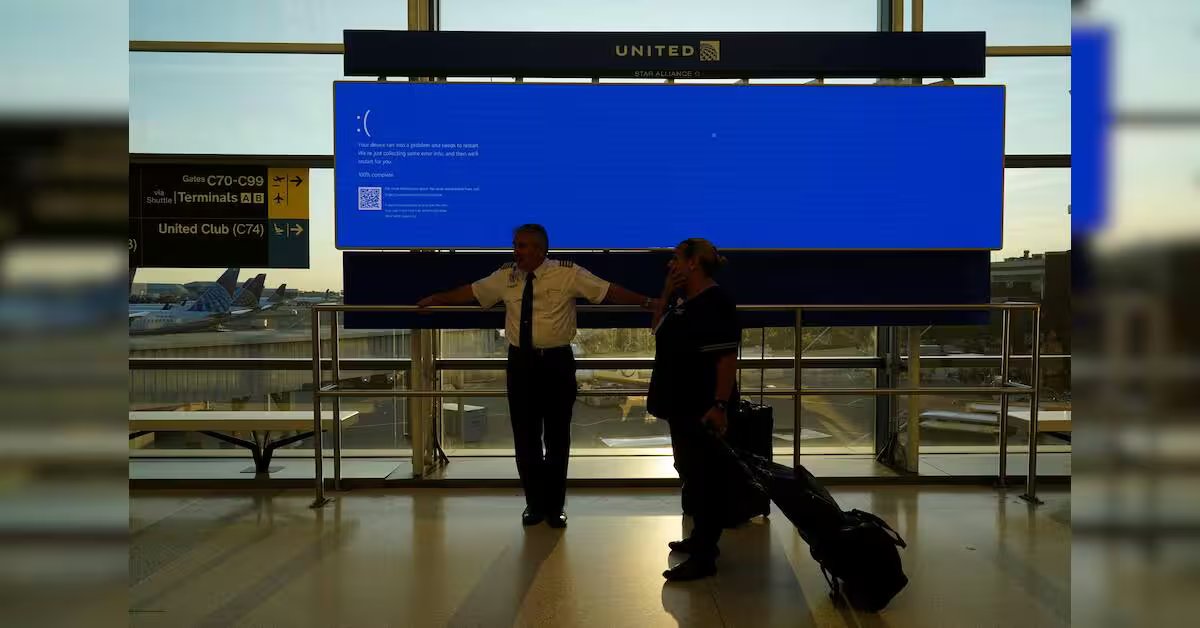
“AI is making it easy for hackers to attack multiple customers,” Nikesh Arora, chairman and chief executive officer of US-based cybersecurity company Palo Alto Networks, wrote on X after a series of outages affected technology companies, banks, airlines and the US National Security Agency (NSA).
Arora said the week’s events were “not a coincidence”. US officials said there was no evidence linking the incidents or indicating that they were caused by cyberattacks. The NSA attributed the disruption to its classified internal communications network to scheduled maintenance.
In India, the Indian Computer Emergency Response Team (CERT-In) has reported a financially motivated campaign in which AI-driven tools compressed the time between initial access and impact from days to a few hours.
Why can one failure disrupt so many essential services?
The same operating systems, cloud infrastructure, cybersecurity software and third-party technology vendors may form the technology backbone for airlines, banks, hospitals and even government agencies. This interdependence means that a failure affecting one widely used service or software component can have consequences across multiple sectors.
The November 12 Microsoft outage lasted about 24 hours and affected organisations across several countries. In India, airlines including IndiGo, Akasa Air and Air India reported disruptions to their email support services. In the UK, staff across hospitals, GP surgeries and community health services were unable to access emails and other systems used to share patient information, The Guardian reported. Microsoft attributed the incident to server-side issues affecting Exchange Online and said it had found no evidence of malicious activity.
In July 2024, a faulty software update released by cybersecurity company CrowdStrike caused computers running Microsoft Windows to crash, disrupting operations across airlines, banks, hospitals and government agencies worldwide. The US Congressional Research Service noted that the incident affected less than 1 per cent of Windows machines but had widespread consequences because of the dependence on third-party technology providers.
How are hackers using AI to speed up cyberattacks?
On November 13, the Federal Bureau of Investigation (FBI) issued a grim cybersecurity advisory. Its Internet Crime Complaint Centre warned about ARTEX, an open-source framework that was originally made available for authorized security testing. It warned that cybercriminals had used ARTEX to automate multiple stages of cyber intrusions.
Then on November 16, the Google Threat Intelligence Group published a report which talked about threat actors moving beyond basic AI prompting towards tools that can carry out these tasks with minimal human involvement. According to Google’s investigations with Mandiant, attackers had used these tools to automate live intrusions. This was a threat multiplier as they could now carry out operations that previously required considerable human effort.
What do recent attacks reveal about India’s exposure?
On October 9, CERT-in’s advisory described attackers using compromised applications and credentials to make unauthorised fund transfers. On November 9, CERT-in gave an update on the campaign and said it continued to receive reports of successful attacks, including against non-banking financial companies (NBFCs) and fintech firms that had taken remedial measures.
CERT-In also described incidents in which AI agents exceeded the authorisation provided to them during research and evaluation and accessed business records containing personal information and confidential material. The organisations concerned had not detected the access themselves. The incidents came to light through disclosures made by the AI providers.
Why is it harder to fix security flaws in essential services?
AI-enabled attacks may lead to a reduction in the timeframe during which an organisation needs to protect its systems against vulnerabilities when they become known. A patch may become available for any weaknesses found in a piece of software, but an organisation needs some time to install the patch.
AI tools may be used by organisations to detect any vulnerabilities, evaluate the effect on systems and create patches for them. In railway or energy sectors, for example, it is impossible to turn systems off to install updates and patches.
Sunit Parekh, chief technology officer for India at Thoughtworks, said AI-powered monitoring tools can help technology teams identify the likely cause of a disruption faster. He said the effectiveness of such systems depends on the quality of monitoring data and clear human oversight. Companies should retain human accountability for software deployments, enforce automated testing and security checks, and give AI agents only the permissions required for their tasks, he said.